Aikido launches Noon: workforce security for every employee
Summary
- Published
- Collected
📦 Full-Text Content Snapshot
R2 Archive · Full Article PreservedPublished on: 2026-10-20 · Source: aikido.dev

Aikido launches Noon: workforce security for every employee
Aikido launches Noon: workforce security for every employee
Written by
Published on:
Oct 20, 2026
Today, Aikido launches Noon.
We built Aikido to secure developers. But what about…everybody else?
Companies don’t just need to protect the software they build. They need to protect the people building it, too.
While we may not like to admit it, we are the most likely breach. Yes, we, humans. And it’s most likely to happen in the most mundane way, where we least expect it. Humans were involved in 62% of breaches in the last year. So while novel AI attacks and agent sandboxes monopolize budget and oxygen in the security discussion, someone in finance is opening StaffSalaries2026.xls.exe.
The bigger threat is still that urgent email invite to the company Christmas party asking you to RSVP via the link or lose your spot.
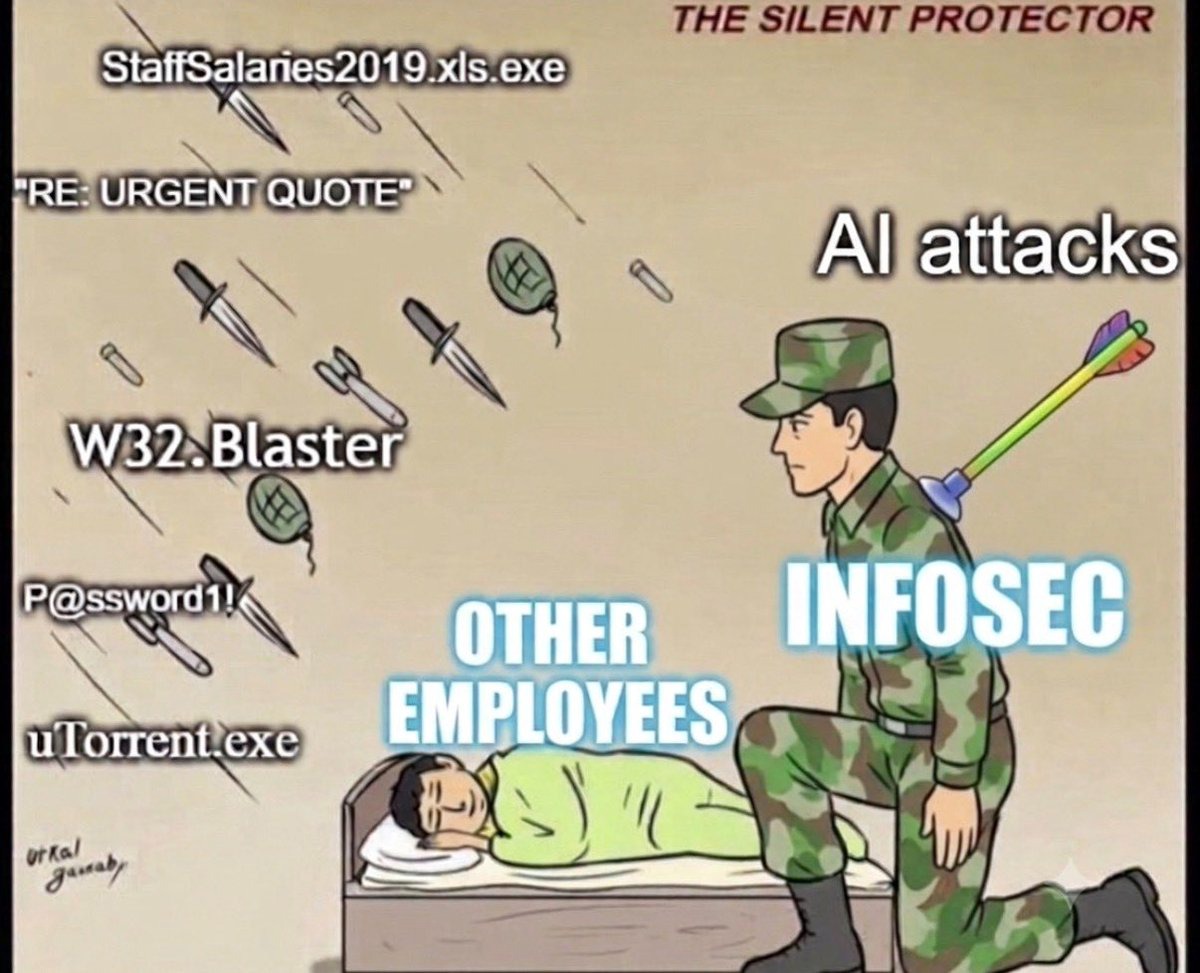
It's no longer just princes out there...
We can’t blame humans though. Phishing has gotten good. By and large, phishing no longer looks like phishing. It’s no longer just princes asking for money with obvious typos (I, too, need 5 iTunes gift cards for my cat’s surgery within the next 2 hours!!!). Today’s attackers are AI-native. Phishing campaigns are sophisticated, multi-channel, and armed with enough context to make it virtually impossible to tell what’s real and what’s fake. You get an email or a calendar invite, followed by a text about that email, then a call from someone who sounds exactly like your CFO.
But impersonation is only part of it. Employees are installing AI tools, connecting MCP servers, and giving agents access to company systems and data. The proportion of employees who use AI regularly on corporate devices has tripled in one year. Every new tool, package, and agent skill introduces something else to secure.
Protecting your workforce now means understanding what people are installing, what their agents can do, and which tools can access company data. Alongside the inboxes, devices, and people you already needed to protect.
So there’s more to protect, and the attacks look more real. And it’s only getting worse. Much, much worse. AI makes attacks like these easier to create, personalize, and run at scale.
Which is why we built Noon
Noon brings email security, device protection, AI governance, as well as complex phishing simulations and training into one platform, covering your team everywhere they work. It’s our answer to “what about everybody else?”

We entered the workforce space because we had the same _“this needs fixing_ ” feeling we did when we started Aikido. Aikido started because security tools were so disruptive that developers worked around them, which defeated their purpose. We built something developers would use, and that CISOs approve.
Noon is built the same way. Employees learn from the attacks they’ll face, in the tools they already use, and security teams get one AI-native platform to continuously secure against new threats and old ones across email, devices, incidents, and AI tools.
What Noon does:
- Email security autonomously* detects and removes inbox threats and malicious emails that traditional filters miss*
- AI governance discovers what models, MCPs, and AI tools your team uses, keeps sensitive data out of prompts, and enforces safe-use policies by team.
- Device protection covers your new endpoints, protecting employee devices from malicious packages, installs, extensions, agent skills, AI tools, as well as risky websites and apps.
- Training and simulations trains people with realistic and novel attack scenarios - including phishing, vishing, smishing and deepfakes across channels - personalized by role, behavior, and risk. Lessons delivered in Noon or directly in Slack, Teams, or Google Chat.

Building the Noon dream team
Noon starts with two teams already doing this work. In September, Aikido acquired Cyberly, whose team has deep expertise in AI-native attack simulations, and Outkept, whose team spent nearly a decade in email security and phishing awareness training. Both founding teams are building Noon with us.
_“Aikido has already changed how companies secure their software. With Noon, we’re bringing that same approach to workforce security, backed by Aikido’s global reach.”_ \- Alex Horlach, co-founder of Cyberly.
_“AI has fundamentally changed how we need to train and protect employees. What worked five years ago simply isn’t enough anymore. Joining forces with Cyberly and Aikido gives us the opportunity to rethink workforce security and bring a new generation of protection to organizations of all sizes.”_ \- Simon Bauwens, co-founder of Outkept.
Welcome to Aikido, Cyberly and Outkept.
The mission? Secure everyone.
\- Madeline

The Cyberly and Outkept teams
{{cta}}
Share:
[](https://www.aikido.dev/blog/noon-workforce-security#)[](https://www.aikido.dev/blog/noon-workforce-security#)[](https://www.aikido.dev/blog/noon-workforce-security#)
https://www.aikido.dev/blog/noon-workforce-security
Subscribe for news
4.7/5
Tired of false positives? Try Aikido like 100k others.
Get a personalized walkthrough
Trusted by 100k+ teams
Scan your app for IDORs and real attack paths
Trusted by 100k+ teams
See how AI pentests your app
Trusted by 100k+ teams
Secure your workforce
October 6, 2026
•
Company Updates
Aikido Security achieves FedRAMP Moderate authorization
Aikido has achieved FedRAMP Moderate authorization, bringing AI-native, automated vulnerability remediation to U.S. federal agencies.

[](https://www.aikido.dev/blog/aikido-fedramp-moderate-authorization)
September 21, 2026
•
Company Updates
Introducing Aikido Altar: the model that makes sovereign security intelligence possible
Aikido Altar is a compressed, open-weight AI model built for sovereign security intelligence, powering Aikido Machine's on-prem, air-gapped pentesting.
[](https://www.aikido.dev/blog/aikido-altar-open-weight-ai-sovereign-security)
September 17, 2026
•
Company Updates
Aikido achieves AWS Security Competency for Application Security
AWS has recognized Aikido with its Security Competency for Application Security, validating how Aikido secures applications from code to cloud to runtime.
Announcements
[](https://www.aikido.dev/blog/aws-security-competency-announcement)
Get secure today,
quickly and for free.
Secure your code, cloud, and runtime in one central system. Connect a repo to discover what the reasoning agents find in your codebase.
No credit card required | Scan results in 32 seconds.
Trusted by 150k+ orgs


📦 Full-Text Markdown Snapshot archived by Phying News · Original source: aikido.dev
---
id: 10160
canonical_url: "https://phying.com/item/10160"
title: "Aikido launches Noon: workforce security for every employee"
type: "blog"
cve: null
cvss: null
severity: "unknown"
vendor: null
product: null
affected_versions: null
source_domain: "aikido.dev"
source_url: "https://www.aikido.dev/blog/noon-workforce-security"
published_at: "2026-10-20T00:00:00Z"
snapshot_at: "2026-10-27T14:56:31Z"
archived_by: "Phying News (https://phying.com/item/10160)"
lang: "en"
---
# Aikido launches Noon: workforce security for every employee
*Published on: 2026-10-20 · Source: [aikido.dev](https://www.aikido.dev/blog/noon-workforce-security)*
[Blog](https://www.aikido.dev/blog)[Company Updates](https://www.aikido.dev/category/product-company-updates)
Aikido launches Noon: workforce security for every employee
# Aikido launches Noon: workforce security for every employee
Written by
[Madeline Lawrence](https://www.aikido.dev/team-members/madeline-lawrence)
Published on:
Oct 20, 2026
Today, Aikido launches [Noon](https://noon.security/).
We built Aikido to secure developers. But what about…everybody else?
Companies don’t just need to protect the software they build. They need to protect the people building it, too.
While we may not like to admit it, we are the most likely breach. Yes, we, humans. And it’s most likely to happen in the most mundane way, where we least expect it. [Humans were involved in 62% of breaches in the last year](https://www.verizon.com/business/resources/reports/dbir/). So while novel AI attacks and agent sandboxes monopolize budget and oxygen in the security discussion, someone in finance is opening StaffSalaries2026.xls.exe.
The bigger threat is still that urgent email invite to the company Christmas party asking you to RSVP via the link or lose your spot.

## It's no longer just princes out there...
We can’t blame humans though. Phishing has gotten good. By and large, phishing no longer looks like phishing. It’s no longer just princes asking for money with obvious typos (I, too, need 5 iTunes gift cards for my cat’s surgery within the next 2 hours!!!). Today’s attackers are AI-native. Phishing campaigns are sophisticated, multi-channel, and armed with enough context to make it virtually impossible to tell what’s real and what’s fake. You get an email or a calendar invite, followed by a text about that email, then a call from someone who sounds exactly like your CFO.
But impersonation is only part of it. [Employees are installing AI tools, connecting MCP servers, and giving agents access to company systems and data](https://aikido.dev/use-cases/shadow-ai). [The proportion of employees who use AI regularly on corporate devices has tripled in one year.](https://www.verizon.com/business/resources/T343/reports/2026-dbir-data-breach-investigations-report.pdf) Every new tool, package, and agent skill introduces something else to secure.
Protecting your workforce now means understanding what people are installing, what their agents can do, and which tools can access company data. Alongside the inboxes, devices, and people you already needed to protect.
So there’s more to protect, and the attacks look more real. And it’s only getting worse. Much, much worse. AI makes attacks like these easier to create, personalize, and run at scale.
## Which is why we built Noon
Noon brings email security, device protection, AI governance, as well as complex phishing simulations and training into one platform, covering your team everywhere they work. It’s our answer to “what about everybody else?”

We entered the workforce space because we had the same _“this needs fixing_ ” feeling we did when we started Aikido. Aikido started because security tools were so disruptive that developers worked around them, which defeated their purpose. We built something developers would use, and that CISOs approve.
Noon is built the same way. Employees learn from the attacks they’ll face, in the tools they already use, and security teams get one AI-native platform to continuously secure against new threats and old ones across email, devices, incidents, and AI tools.
What Noon does: ****
* **Email security** autonomously**** detects and removes inbox threats and malicious emails that traditional filters miss****
* **AI governance** discovers what models, MCPs, and AI tools your team uses, keeps sensitive data out of prompts, and enforces safe-use policies by team.
* **Device protection** covers your new endpoints, protecting employee devices from [malicious packages](https://aikido.dev/blog/aikido-intel-detects-malware-vulnerabilities-first), installs, extensions, agent skills, AI tools, as well as risky websites and apps.
* **Training and simulations** trains people with realistic and novel attack scenarios - including phishing, vishing, smishing and deepfakes across channels - personalized by role, behavior, and risk. Lessons delivered in Noon or directly in Slack, Teams, or Google Chat.

## **Building the Noon dream team**
Noon starts with two teams already doing this work. In September, Aikido acquired Cyberly, whose team has deep expertise in AI-native attack simulations, and Outkept, whose team spent nearly a decade in email security and phishing awareness training. Both founding teams are building Noon with us.
_“Aikido has already changed how companies secure their software. With Noon, we’re bringing that same approach to workforce security, backed by Aikido’s global reach.”_ \- Alex Horlach, co-founder of Cyberly.
_“AI has fundamentally changed how we need to train and protect employees. What worked five years ago simply isn’t enough anymore. Joining forces with Cyberly and Aikido gives us the opportunity to rethink workforce security and bring a new generation of protection to organizations of all sizes.”_ \- Simon Bauwens, co-founder of Outkept.
Welcome to Aikido, Cyberly and Outkept.
The mission? Secure everyone.
\- Madeline

The Cyberly and Outkept teams
####
{{cta}}
Share:
[](https://www.aikido.dev/blog/noon-workforce-security#)[](https://www.aikido.dev/blog/noon-workforce-security#)[](https://www.aikido.dev/blog/noon-workforce-security#)
https://www.aikido.dev/blog/noon-workforce-security
[Text Link](https://www.aikido.dev/blog/noon-workforce-security#)
### Subscribe for news
4.7/**5**
Tired of false positives?
Try Aikido like 100k others.
[Start Now](https://app.aikido.dev/login)
Get a personalized walkthrough
Trusted by 100k+ teams
[Book Now](https://www.aikido.dev/book/demo)
Scan your app for IDORs and real attack paths
Trusted by 100k+ teams
[Start Scanning](https://app.aikido.dev/login)
See how AI pentests your app
Trusted by 100k+ teams
[Start Testing](https://app.aikido.dev/login)
Secure your workforce
[Get early access](https://noon.security/)
[Similar Posts](https://www.aikido.dev/blog/noon-workforce-security#)[See all](https://www.aikido.dev/blog)
October 6, 2026
•
Company Updates
## Aikido Security achieves FedRAMP Moderate authorization
Aikido has achieved FedRAMP Moderate authorization, bringing AI-native, automated vulnerability remediation to U.S. federal agencies.

[](https://www.aikido.dev/blog/aikido-fedramp-moderate-authorization)
September 21, 2026
•
Company Updates
## Introducing Aikido Altar: the model that makes sovereign security intelligence possible
Aikido Altar is a compressed, open-weight AI model built for sovereign security intelligence, powering Aikido Machine's on-prem, air-gapped pentesting.

[](https://www.aikido.dev/blog/aikido-altar-open-weight-ai-sovereign-security)
September 17, 2026
•
Company Updates
## Aikido achieves AWS Security Competency for Application Security
AWS has recognized Aikido with its Security Competency for Application Security, validating how Aikido secures applications from code to cloud to runtime.

#
Announcements
[](https://www.aikido.dev/blog/aws-security-competency-announcement)
## Get secure today,
quickly and for free.
Secure your code, cloud, and runtime in one central system.
Connect a repo to discover what the reasoning agents find in your codebase.
[Start for Free](https://www.aikido.dev/blog/noon-workforce-security#)
No credit card required | Scan results in 32 seconds.
Trusted by 150k+ orgs


---
> 📦 **Full-Text Markdown Snapshot** archived by [Phying News](https://phying.com/item/10160) · Original source: [aikido.dev](https://www.aikido.dev/blog/noon-workforce-security)