CISA’s VDP platform: Five years of collaborative defense
Summary
- Published
- Collected
📦 Full-Text Content Snapshot
R2 Archive · Full Article PreservedPublished on: 2026-10-22 · Source: bugcrowd.com
CISA’s VDP platform: Five years of collaborative defense
October 22, 2026 | By Erica Azad
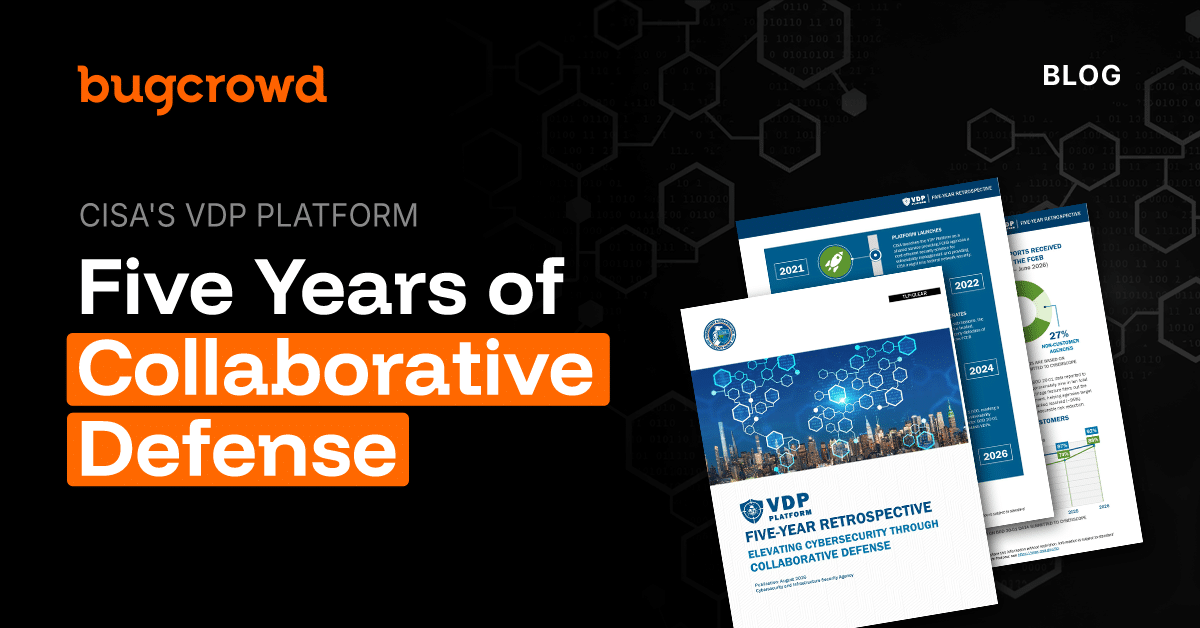
Bugcrowd and EnDyna have powered CISA’s VDP Platform since its launch in July 2021, providing the infrastructure, triage expertise, and researcher community that make the shared service work at federal scale. What started with eleven Federal Civilian Executive Branch (FCEB) agencies has grown into a program supporting more than 60 customer agencies, all running on the same centralized platform for intake, triage, remediation tracking, and researcher communication.
That growth hasn’t just been about signing up more agencies. Bugcrowd’s role has been to make vulnerability disclosure sustainable for teams that often don’t have the internal bandwidth to manage it alone: dedicated triage teams filter out noise, retesting functionality confirms remediations actually worked, and an integrated bug bounty capability gives agencies an on-ramp to incentivized, crowdsourced testing whenever they’re ready for it.
Five years in, the numbers tell the story of what that partnership has produced across the federal space:
- Nearly 45,000 total submissions
- More than 5,700 valid disclosures
- Over 5,300 vulnerabilities remediated.
“Five years ago, we set out to prove that preemptive security could work at a federal scale. This report is proof of that,” says Dave Gerry, Bugcrowd CEO. “Every valid disclosure and every remediated vulnerability represents a real reduction in risk for the agencies that serve the American public, and it’s a testament to what happens when the government and the security research community work together with a shared sense of purpose.”
Highlights from the report
There are a few numbers from the past five years that stand out.
Total submissions have grown from 2,187 in the Platform’s first year to 44,493 cumulatively through June 2026 , with nearly 6,000 of those representing valid, actionable disclosures. The Platform’s triage process filters out roughly 87% of inactionable reports before they ever reach an agency, and of the vulnerabilities that are validated, about 95% are ultimately marked resolved.
The researcher community behind those numbers has also scaled significantly, growing to nearly 10,000 unique contributors who’ve collectively engaged with an average of 1.6 FCEB programs each.
The most commonly reported vulnerability classes are:
- Cross-site scripting
- Sensitive data exposure
- Server-side injection
Bug bounties have also become a meaningful part of the Platform’s value: 15 events run to date have paid out $1.3 million in total rewards, identified 532 vulnerabilities, and attracted 483 researchers. One customer put it simply: _“the bug bounty program helps identify high-impact vulnerabilities more quickly through competitive participation, freeing up internal pen testing teams to focus on deeper, more complex attack simulations.”_
From mandate to momentum: BOD 20-01 in practice
In 2020, CISA issued Binding Operational Directive 20-01, requiring every FCEB agency to develop and publish a vulnerability disclosure policy. CISA’s VDP Platform was built to give agencies a shared, ready-made way to comply with BOD 20-01 without having to stand up their own intake and triage operations from scratch. Nearly 75% of all vulnerability disclosure reports that have been submitted across the federal government were submitted directly through agencies using the VDP Platform powered by Bugcrowd and EnDyna.
A FedRAMP authorized solution
Earlier this year, Bugcrowd announced we achieved FedRAMP Moderate Authorization, sponsored by CISA. This means that federal agencies can now rapidly deploy Bugcrowd’s offensive security testing solutions at scale. This extends beyond vulnerability disclosure. To learn more about Bugcrowd’s solutions for government, check out the solutions guide.
Get involved
The five-year retrospective is a clear look at what collaborative defense delivers when it’s backed by the right infrastructure and the right community. For more information about the VDP Platform or how to get your agency involved, contact CISA’s VDP Platform team at VDPPlatform@cisa.dhs.gov.
Tags:
- BOD 20-01
- bug bounty
- bugcrowd
- CISA
- collaborative defense
- crowdsourced security
- EnDyna
- FCEB agencies
- federal cybersecurity
- FedRAMP
- FedRAMP Moderate
- government security
- VDP Platform
- vulnerability disclosure
- vulnerability disclosure program
More from the blog
Weird ways to hide shellcode
By Jack Barradell-Johns I Principal Red Team Manager, Oct 15, 2026
Evolving our submission accuracy and throttling controls to protect triage speed
By Trey Ford, Oct 08, 2026
How to secure and build trust in your APIs through Savant Probe
By Erica Azad, Oct 06, 2026
Subscribe for updates
📦 Full-Text Markdown Snapshot archived by Phying News · Original source: bugcrowd.com
--- id: 10394 title: "CISA’s VDP platform: Five years of collaborative defense" cve: null cvss: null severity: "unknown" vendor: null product: null affected_versions: null source_domain: "bugcrowd.com" source_url: "https://www.bugcrowd.com/blog/cisas-vdp-platform-five-years-of-collaborative-defense/" published_at: "2026-10-22T16:15:20Z" snapshot_at: "2026-10-28T23:56:34Z" archived_by: "Phying News (https://phying.com/item/10394)" lang: en --- # CISA’s VDP platform: Five years of collaborative defense *Published on: 2026-10-22 · Source: [bugcrowd.com](https://www.bugcrowd.com/blog/cisas-vdp-platform-five-years-of-collaborative-defense/)* [Bugcrowd News](https://www.bugcrowd.com/blog/?t__category=26) # CISA’s VDP platform: Five years of collaborative defense October 22, 2026 | By [Erica Azad](https://www.bugcrowd.com/blog/?a__author=74)  [Back to blog](https://www.bugcrowd.com/blog/) Bugcrowd and EnDyna have powered CISA’s VDP Platform since its launch in July 2021, providing the infrastructure, triage expertise, and researcher community that make the shared service work at federal scale. What started with eleven Federal Civilian Executive Branch (FCEB) agencies has grown into a program supporting more than 60 customer agencies, all running on the same centralized platform for intake, triage, remediation tracking, and researcher communication. That growth hasn’t just been about signing up more agencies. Bugcrowd’s role has been to make vulnerability disclosure sustainable for teams that often don’t have the internal bandwidth to manage it alone: dedicated triage teams filter out noise, retesting functionality confirms remediations actually worked, and an integrated bug bounty capability gives agencies an on-ramp to incentivized, crowdsourced testing whenever they’re ready for it. Five years in, the numbers tell the story of what that partnership has produced across the federal space: * Nearly 45,000 total submissions * More than 5,700 valid disclosures * Over 5,300 vulnerabilities remediated. “Five years ago, we set out to prove that preemptive security could work at a federal scale. This report is proof of that,” says Dave Gerry, Bugcrowd CEO. “Every valid disclosure and every remediated vulnerability represents a real reduction in risk for the agencies that serve the American public, and it’s a testament to what happens when the government and the security research community work together with a shared sense of purpose.” ## Highlights from the report There are a few numbers from the past five years that stand out. Total submissions have grown **from 2,187 in the Platform’s first year to 44,493 cumulatively through June 2026** , with nearly 6,000 of those representing valid, actionable disclosures. The Platform’s triage process filters out roughly 87% of inactionable reports before they ever reach an agency, and of the vulnerabilities that are validated, about 95% are ultimately marked resolved. The researcher community behind those numbers has also scaled significantly, growing to **nearly 10,000 unique contributors** who’ve collectively engaged with an average of 1.6 FCEB programs each. The most commonly reported vulnerability classes are: 1. Cross-site scripting 2. Sensitive data exposure 3. Server-side injection Bug bounties have also become a meaningful part of the Platform’s value: 15 events run to date have paid out $1.3 million in total rewards, identified 532 vulnerabilities, and attracted 483 researchers. One customer put it simply: _“the bug bounty program helps identify high-impact vulnerabilities more quickly through competitive participation, freeing up internal pen testing teams to focus on deeper, more complex attack simulations.”_ ## From mandate to momentum: BOD 20-01 in practice In 2020, CISA issued Binding Operational Directive 20-01, requiring every FCEB agency to develop and publish a vulnerability disclosure policy. CISA’s VDP Platform was built to give agencies a shared, ready-made way to comply with BOD 20-01 without having to stand up their own intake and triage operations from scratch. Nearly 75% of all vulnerability disclosure reports that have been submitted across the federal government were submitted directly through agencies using the VDP Platform powered by Bugcrowd and EnDyna. ## A FedRAMP authorized solution Earlier this year, Bugcrowd announced we achieved FedRAMP Moderate Authorization, sponsored by CISA. This means that federal agencies can now rapidly deploy Bugcrowd’s offensive security testing solutions at scale. This extends beyond vulnerability disclosure. To learn more about Bugcrowd’s solutions for government, check out the [solutions guide](https://www.bugcrowd.com/resources/guide/bugcrowd-for-government/). ## Get involved The five-year retrospective is a clear look at what collaborative defense delivers when it’s backed by the right infrastructure and the right community. For more information about the VDP Platform or how to get your agency involved, contact CISA’s VDP Platform team at VDPPlatform@cisa.dhs.gov. Tags: * [BOD 20-01](https://www.bugcrowd.com/blog/?t__post_tag=804) * [bug bounty](https://www.bugcrowd.com/blog/?t__post_tag=36) * [bugcrowd](https://www.bugcrowd.com/blog/?t__post_tag=45) * [CISA](https://www.bugcrowd.com/blog/?t__post_tag=788) * [collaborative defense](https://www.bugcrowd.com/blog/?t__post_tag=1890) * [crowdsourced security](https://www.bugcrowd.com/blog/?t__post_tag=41) * [EnDyna](https://www.bugcrowd.com/blog/?t__post_tag=1891) * [FCEB agencies](https://www.bugcrowd.com/blog/?t__post_tag=1892) * [federal cybersecurity](https://www.bugcrowd.com/blog/?t__post_tag=1109) * [FedRAMP](https://www.bugcrowd.com/blog/?t__post_tag=1888) * [FedRAMP Moderate](https://www.bugcrowd.com/blog/?t__post_tag=1889) * [government security](https://www.bugcrowd.com/blog/?t__post_tag=1601) * [VDP Platform](https://www.bugcrowd.com/blog/?t__post_tag=1887) * [vulnerability disclosure](https://www.bugcrowd.com/blog/?t__post_tag=61) * [vulnerability disclosure program](https://www.bugcrowd.com/blog/?t__post_tag=34) ### More from the blog  [ Red Teaming ](https://www.bugcrowd.com/blog/?t__category=1225) #### Weird ways to hide shellcode By Jack Barradell-Johns I Principal Red Team Manager, Oct 15, 2026 [ Read More ](https://www.bugcrowd.com/blog/weird-ways-to-hide-shellcode/)  [ Bugcrowd News ](https://www.bugcrowd.com/blog/?t__category=26) #### Evolving our submission accuracy and throttling controls to protect triage speed By Trey Ford, Oct 08, 2026 [ Read More ](https://www.bugcrowd.com/blog/evolving-our-submission-accuracy-and-throttling-controls-to-protect-triage-speed/)  [ Bugcrowd Platform ](https://www.bugcrowd.com/blog/?t__category=507) #### How to secure and build trust in your APIs through Savant Probe By Erica Azad, Oct 06, 2026 [ Read More ](https://www.bugcrowd.com/blog/how-to-secure-and-build-trust-in-your-apis-through-savant-probe/) ## Subscribe for updates --- > 📦 **Full-Text Markdown Snapshot** archived by [Phying News](https://phying.com/item/10394) · Original source: [bugcrowd.com](https://www.bugcrowd.com/blog/cisas-vdp-platform-five-years-of-collaborative-defense/)